Featured Insight
Understanding how exposed credentials become one of the most common real-world security risks.
Did They Lose Their Keys? A Black Box Pentest Adventure
All Case Studies & Expert Insights
Deep dive into solutions and cybersecurity topics with our experts
Small devices, big risk: what the OpenAI meeting room case means for NZ organisations
A covert recording device found in an OpenAI meeting room highlights a security risk that traditional cyber defences can miss. Learn how inexpensive hardware and AI-assisted development make eavesdropping easier, and how organisations can protect sensitive conversations.
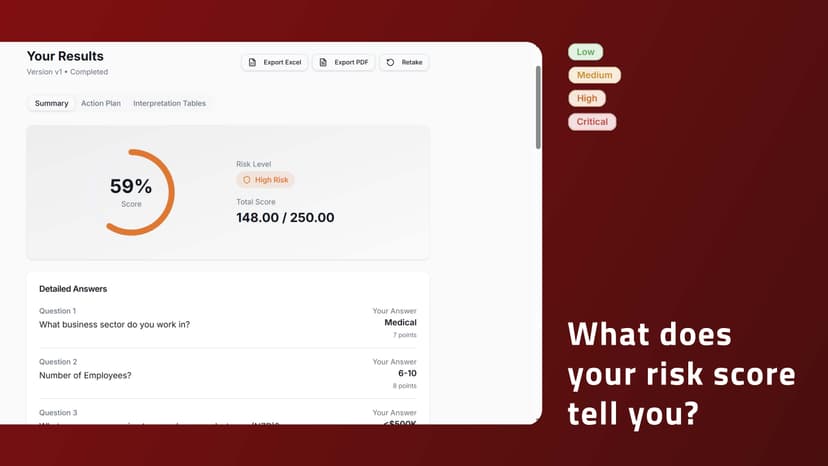
LiveRisk: How to Assess Your Organisation's Cybersecurity Risks (FREE Assessment)
Not sure where to start with cybersecurity? LiveRisk helps small New Zealand organisations understand their cybersecurity risks, interpret their risk scores and ratings, and prioritise practical improvements.
Project Glasswing: What It Means for Cybersecurity
Project Glasswing goes beyond its high-profile launch partners, with funding for open-source security, AI access for maintainers and new governance measures. But the initiative also raises questions about access, workload and who is responsible for fixing the vulnerabilities AI finds.
Claude Mythos: What Its Low Cost Means for Cybersecurity
Claude Mythos has been portrayed as requiring nation-state-level resources to replicate. The reality is more concerning: AI-assisted vulnerability discovery can cost as little as $50, potentially putting powerful offensive capabilities within reach of a much broader range of actors.

Why Secure Large File Transfer Remains a Challenge for Modern Organisations (Webinar)
Secure file transfer is a growing challenge for organisations as email limits and unmanaged sharing tools introduce security, compliance and governance risks. Explore how organisations can maintain control, visibility and security when sharing large or sensitive files.
Pen Testing: Trust Me Bro(ker)
A penetration test uncovered a hidden internal message broker that exposed unauthorised access due to insecure default configurations. This article explores how assumptions about “trusted internal systems” can create significant security risk.